Crypto and Card-Stealing Malware Hits Websites Across 178 Organizations
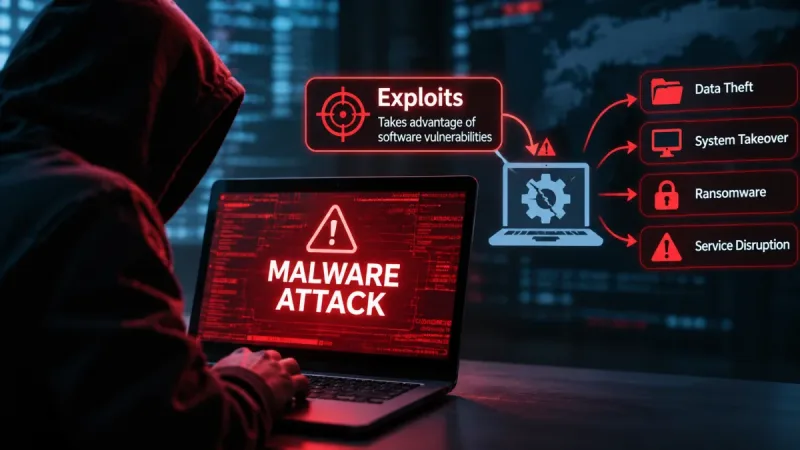
Attackers used compromised website scripts to expose visitors to cryptocurrency theft and credit card skimming on November 16, security researchers found. Ledger and Coinpass were among 178 organizations whose website scripts carried malicious code, highlighting the financial risks that shared technology providers can spread across otherwise unrelated businesses.
Security researcher Scott Helme’s investigation identified 188 infected JavaScript files after examining 1,611 scripts associated with website experimentation platform Optimizely. The affected organizations included trading businesses IG, Interactive Investor and TMS Brokers, alongside companies outside financial services. The organization count does not establish how many visitors encountered the malware or lost money.
Trusted Scripts Became a Theft Channel
Optimizely helps businesses test website changes through scripts that run inside visitors’ browsers. Attackers inserted malicious JavaScript into customer projects, allowing trusted website components to load their theft tools. That distribution method exposed visitors through familiar business websites, rather than requiring them to follow links to fraudulent pages.
The malware could replace legitimate cryptocurrency wallet addresses with addresses controlled by attackers, including when visitors copied payment details. For example, someone copying a deposit address could unknowingly paste a different destination into a wallet application. Researchers also found functionality targeting Bitcoin, Ethereum, Solana and several other cryptocurrency networks.
Payment Details Also Targeted
Separately, technical analysis found that the malware monitored website forms and payment requests for card numbers, expiration dates and security codes. It could transmit captured details to the attacker’s server. However, the analyzed code could not read card fields inside payment frames hosted on a different origin, limiting that collection method.
Optimizely said an unauthorized party exploited a vulnerability in its Experimentation service to add malicious code to customer projects. The company said it fixed the vulnerability, removed injected code and secured affected accounts. Helme’s monitoring found only one previously infected script still carrying malware at 9:52 p.m. UTC on November 16.
The cleanup reduced the immediate exposure, but the financial impact remains uncertain. Researchers identified cryptocurrency transfers involving attacker wallets, although available blockchain activity does not establish a complete victim-loss figure. The incident underscores how compromised browser scripts can threaten both digital-asset transfers and conventional online payments through the same attack.